NetRise Platform
Supply Chain Security Made Easy
The most comprehensive solution for inventory, security visibility, and risk mitigation across your software landscape.
Trust But Verify: The Hidden Dangers of Blind Trust in Software
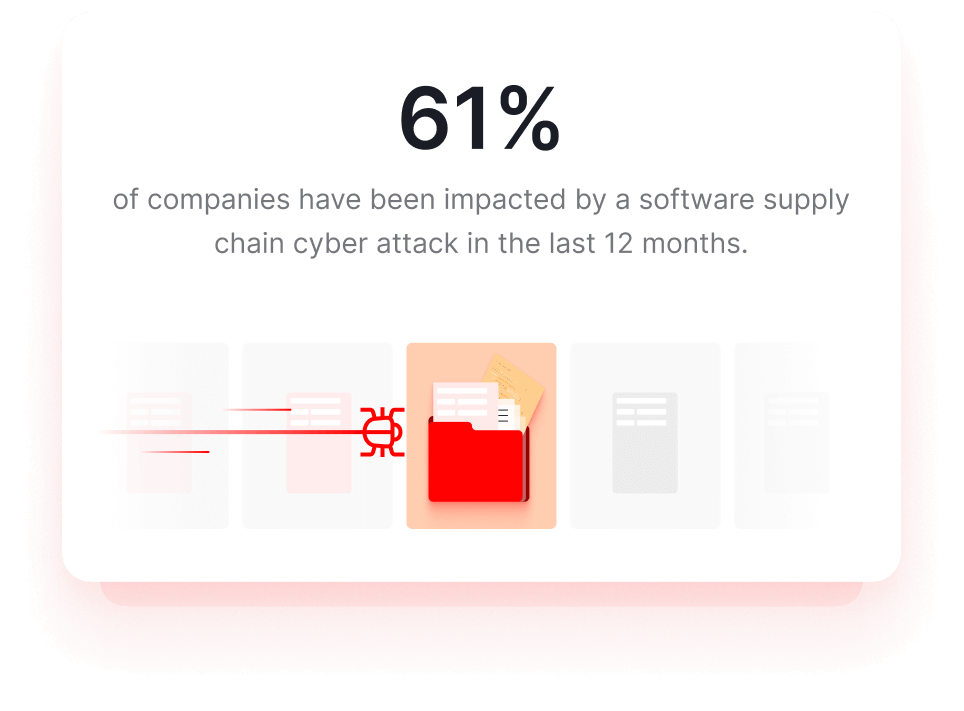
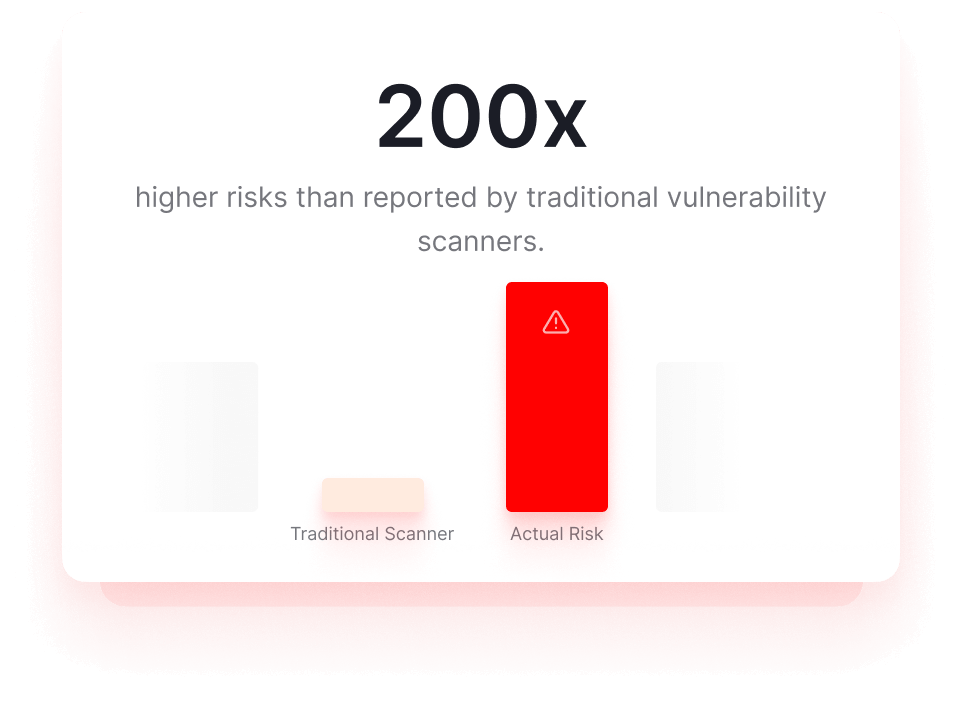
Software powers the modern world—whether it’s third-party tools, open-source code, or in-house applications. But relying on software comes with risks. Many organizations blindly trust their software’s security, only to face vulnerabilities and breaches.
The NetRise Platform provides unmatched visibility into your software supply chain, helping you identify and manage risks across all your assets.
The NetRise Platform Overview
The most complete SBOM generation and software inventory in the market.
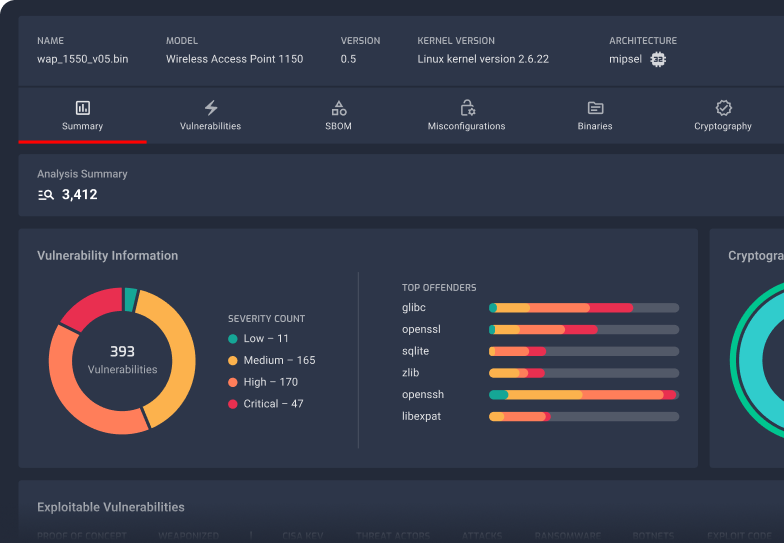
Analyze, discover, and inventory every software component in your organization in a single platform. The NetRise Platform leverages industry-leading binary asset analysis to provide unprecedented visibility into software risk for both software creators and owners alike.
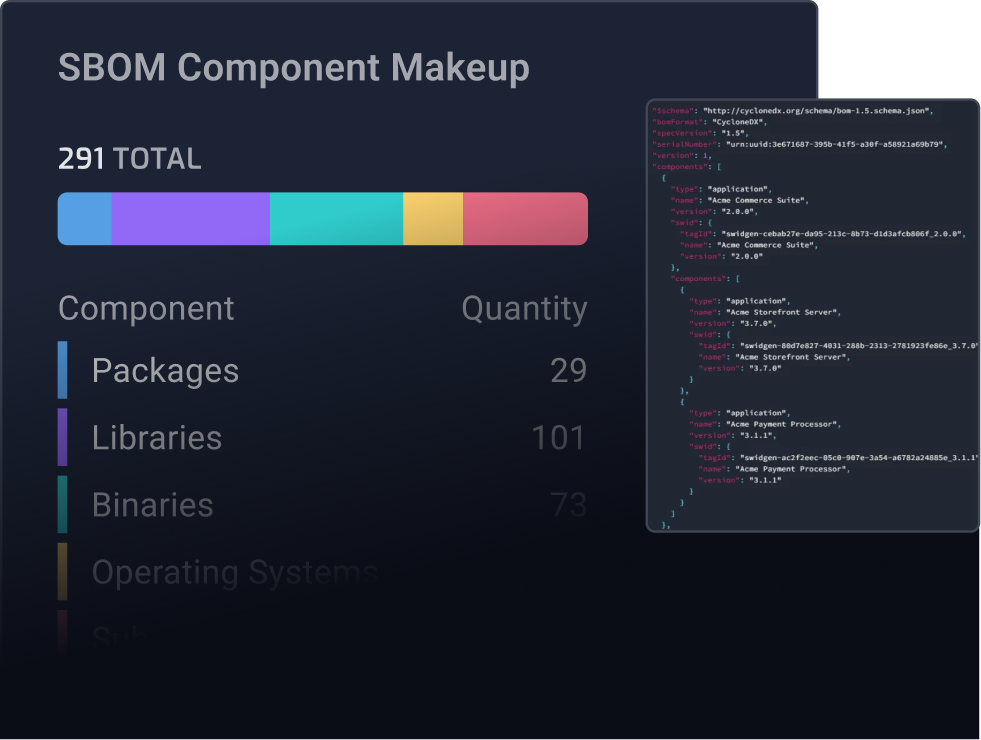
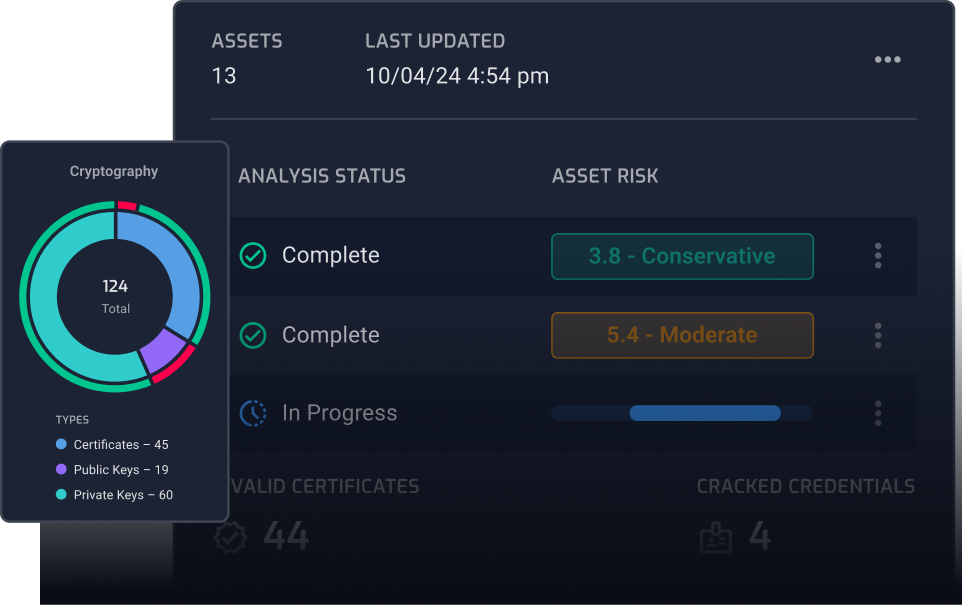
The widest enterprise software coverage available.
The NetRise Platform provides coverage for more asset classes than any other solution in the industry, including devices, operating systems, software packages, containers, individual binaries, and more.
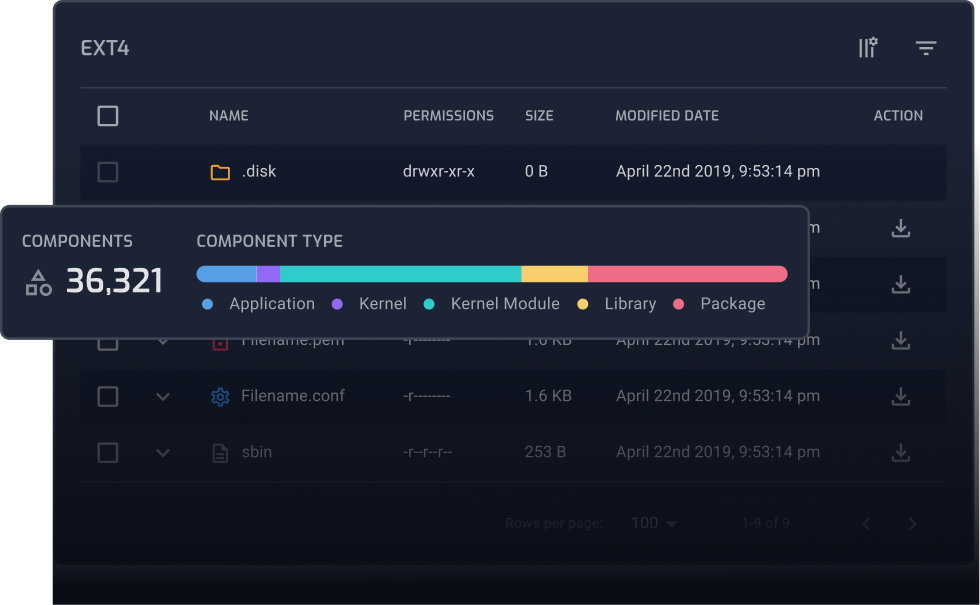
Strengthen security by detecting and addressing software risks.
Better SBOM generation and software visibility enhance vulnerability and risk identification. Comprehensive reports highlight major risks and suggest known fixes. NetRise Trace also enables advanced natural language searches to detect unknown threats.
Customer Use Cases

Inventory and Manage Software Assets
Build SBOMs to inventory all software assets including applications, operating systems, containers, and firmware. Continuously monitor the software supply chain across the enterprise.

Software Procurement Evaluation
Easily analyze and compare the software risk levels of different vendor software as part of the procurement process for every purchase.

Ensure Secure Software Configurations
Evaluate more than just vulnerabilities. Consider non-CVE risks in your software supply chain security posture improvement efforts.

Software License Management
Components are matched to any associated open-source or third-party licenses, allowing you to prove compliance with raw data.

Prioritize Software Risks Across All Assets
Prioritize vulnerabilities and other non-CVE software risks across all software assets.

Test New Compiled Software for Risks
Test all compiled and interpreted code during the development process to identify and prioritize software supply chain risks.